

Our approach
What we cover
We draft and review the legal documents your data protection obligations require: privacy policies (website-facing and employee-facing), data processing agreements with suppliers and processors, data protection clauses in commercial contracts, and advice on handling data subject access requests. We also advise on general UK GDPR compliance questions that arise in the course of running your business.
How we work with you
The starting point is usually an assessment of your current documents and processes. Many SMEs have a privacy policy they adopted in 2018, and haven't touched since. Their contracts with software providers and other suppliers don't include data processing agreements. They have no process for responding to a data subject access request. Each of those gaps is a real legal exposure.
We work through what you need in a logical order: usually starting with the documents your website and employee relationships require, then looking at your supplier contracts, then addressing any gaps in your internal processes. Where data protection comes up in a commercial contract or transaction (buyers increasingly run data protection due diligence), we advise on that too.
All work is on a fixed fee, agreed before we start.
Who we work with
Almost every business collects personal data: website visitors, email subscribers, employees, clients and prospective clients. That's why data protection isn't something you can put off until a regulator asks. In practice, most of our data protection clients are founder-led agencies, tech businesses and high-growth companies for whom personal data is a routine part of how they operate.
Businesses approaching a fundraise or sale are increasingly finding that data protection due diligence is part of the process. Having your documents in order before that conversation starts matters. We can also help businesses that have received a data subject access request and aren't sure how to respond.
Pricing

Fixed-fee project

Available via subscription
Case Studies
Hear from our clients

Meet the team
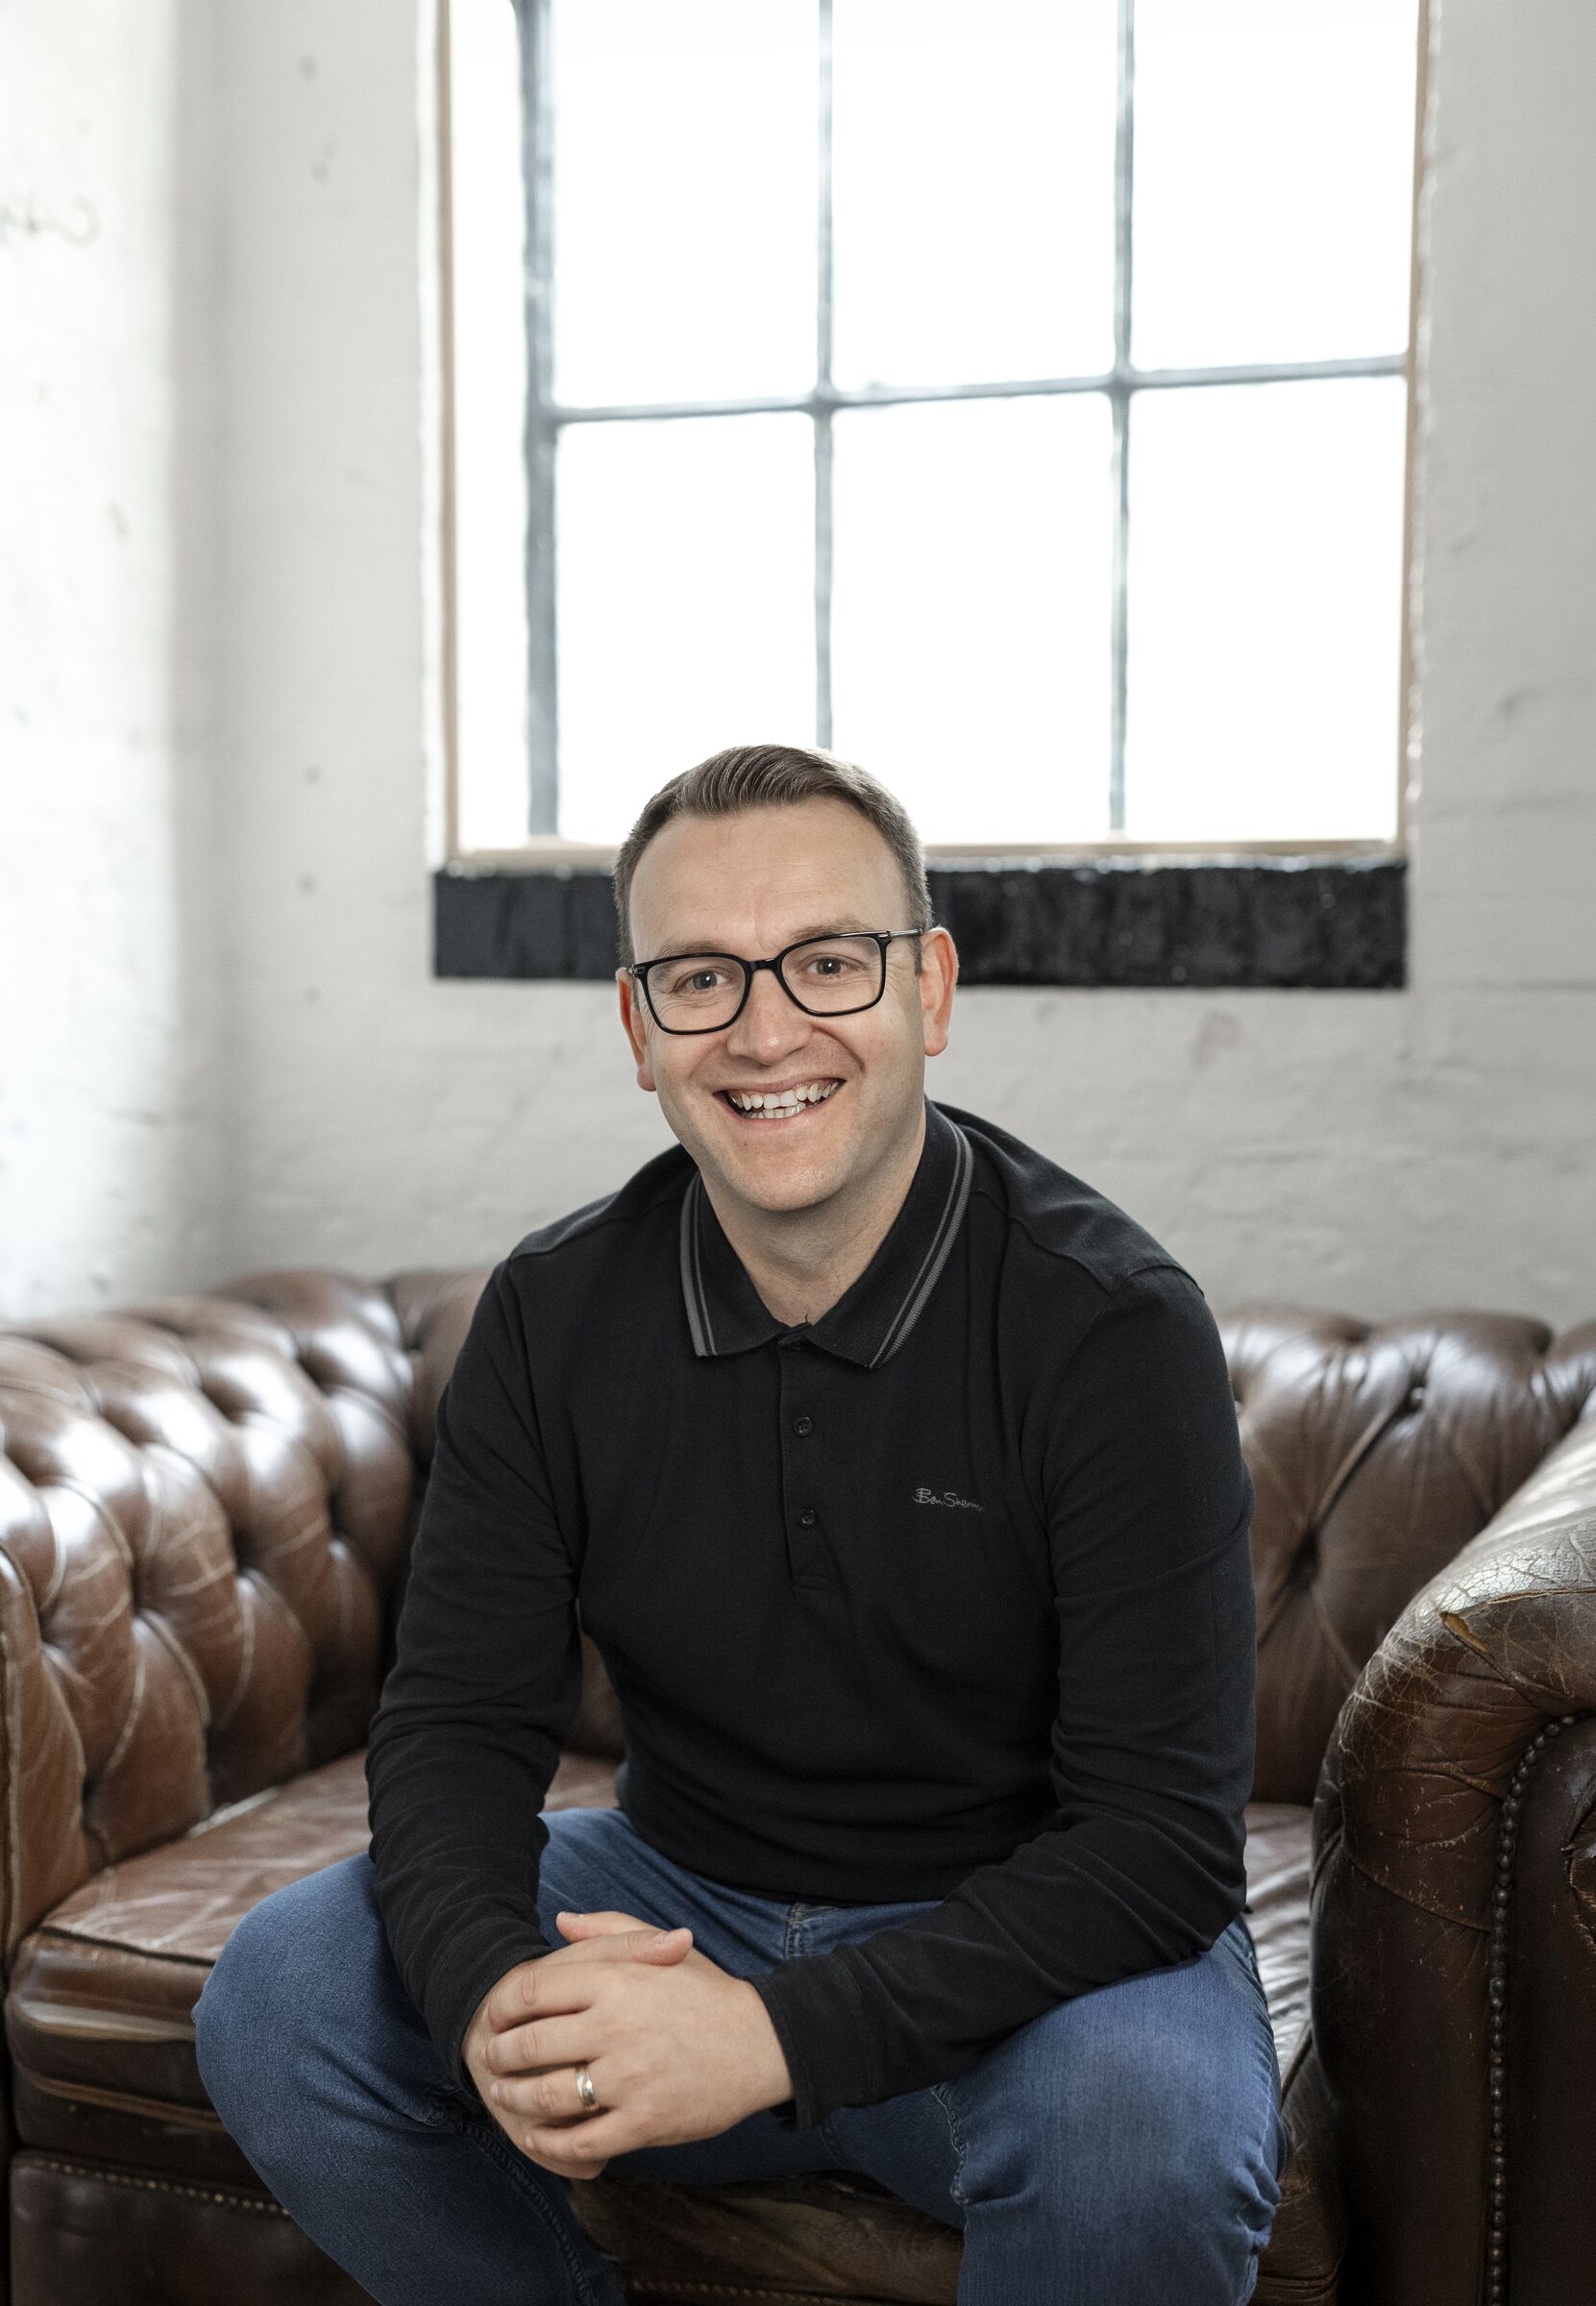


Craig is a corporate and commercial solicitor at Tend Legal, working with founders, business owners and leadership teams as they build, grow and protect their businesses.
He advises on a wide range of matters: mergers and acquisitions, shareholder agreements, company structures, governance and commercial contracts of all kinds. Craig also has a particular interest in intellectual property, and regularly advises on trademark and copyright matters. His IP work has included a matter involving a Premier League and England international footballer, and advising on a copyright assignment connected to a well-known album cover.
Down-to-earth and easy to work with, Craig places a strong emphasis on clear communication and making sure clients feel confident about the decisions they're making. He works closely with agency and commercial clients, acting as an accessible part of their wider advisory team.
Outside of work, Craig is a keen football fan and enjoys spending time with his family.
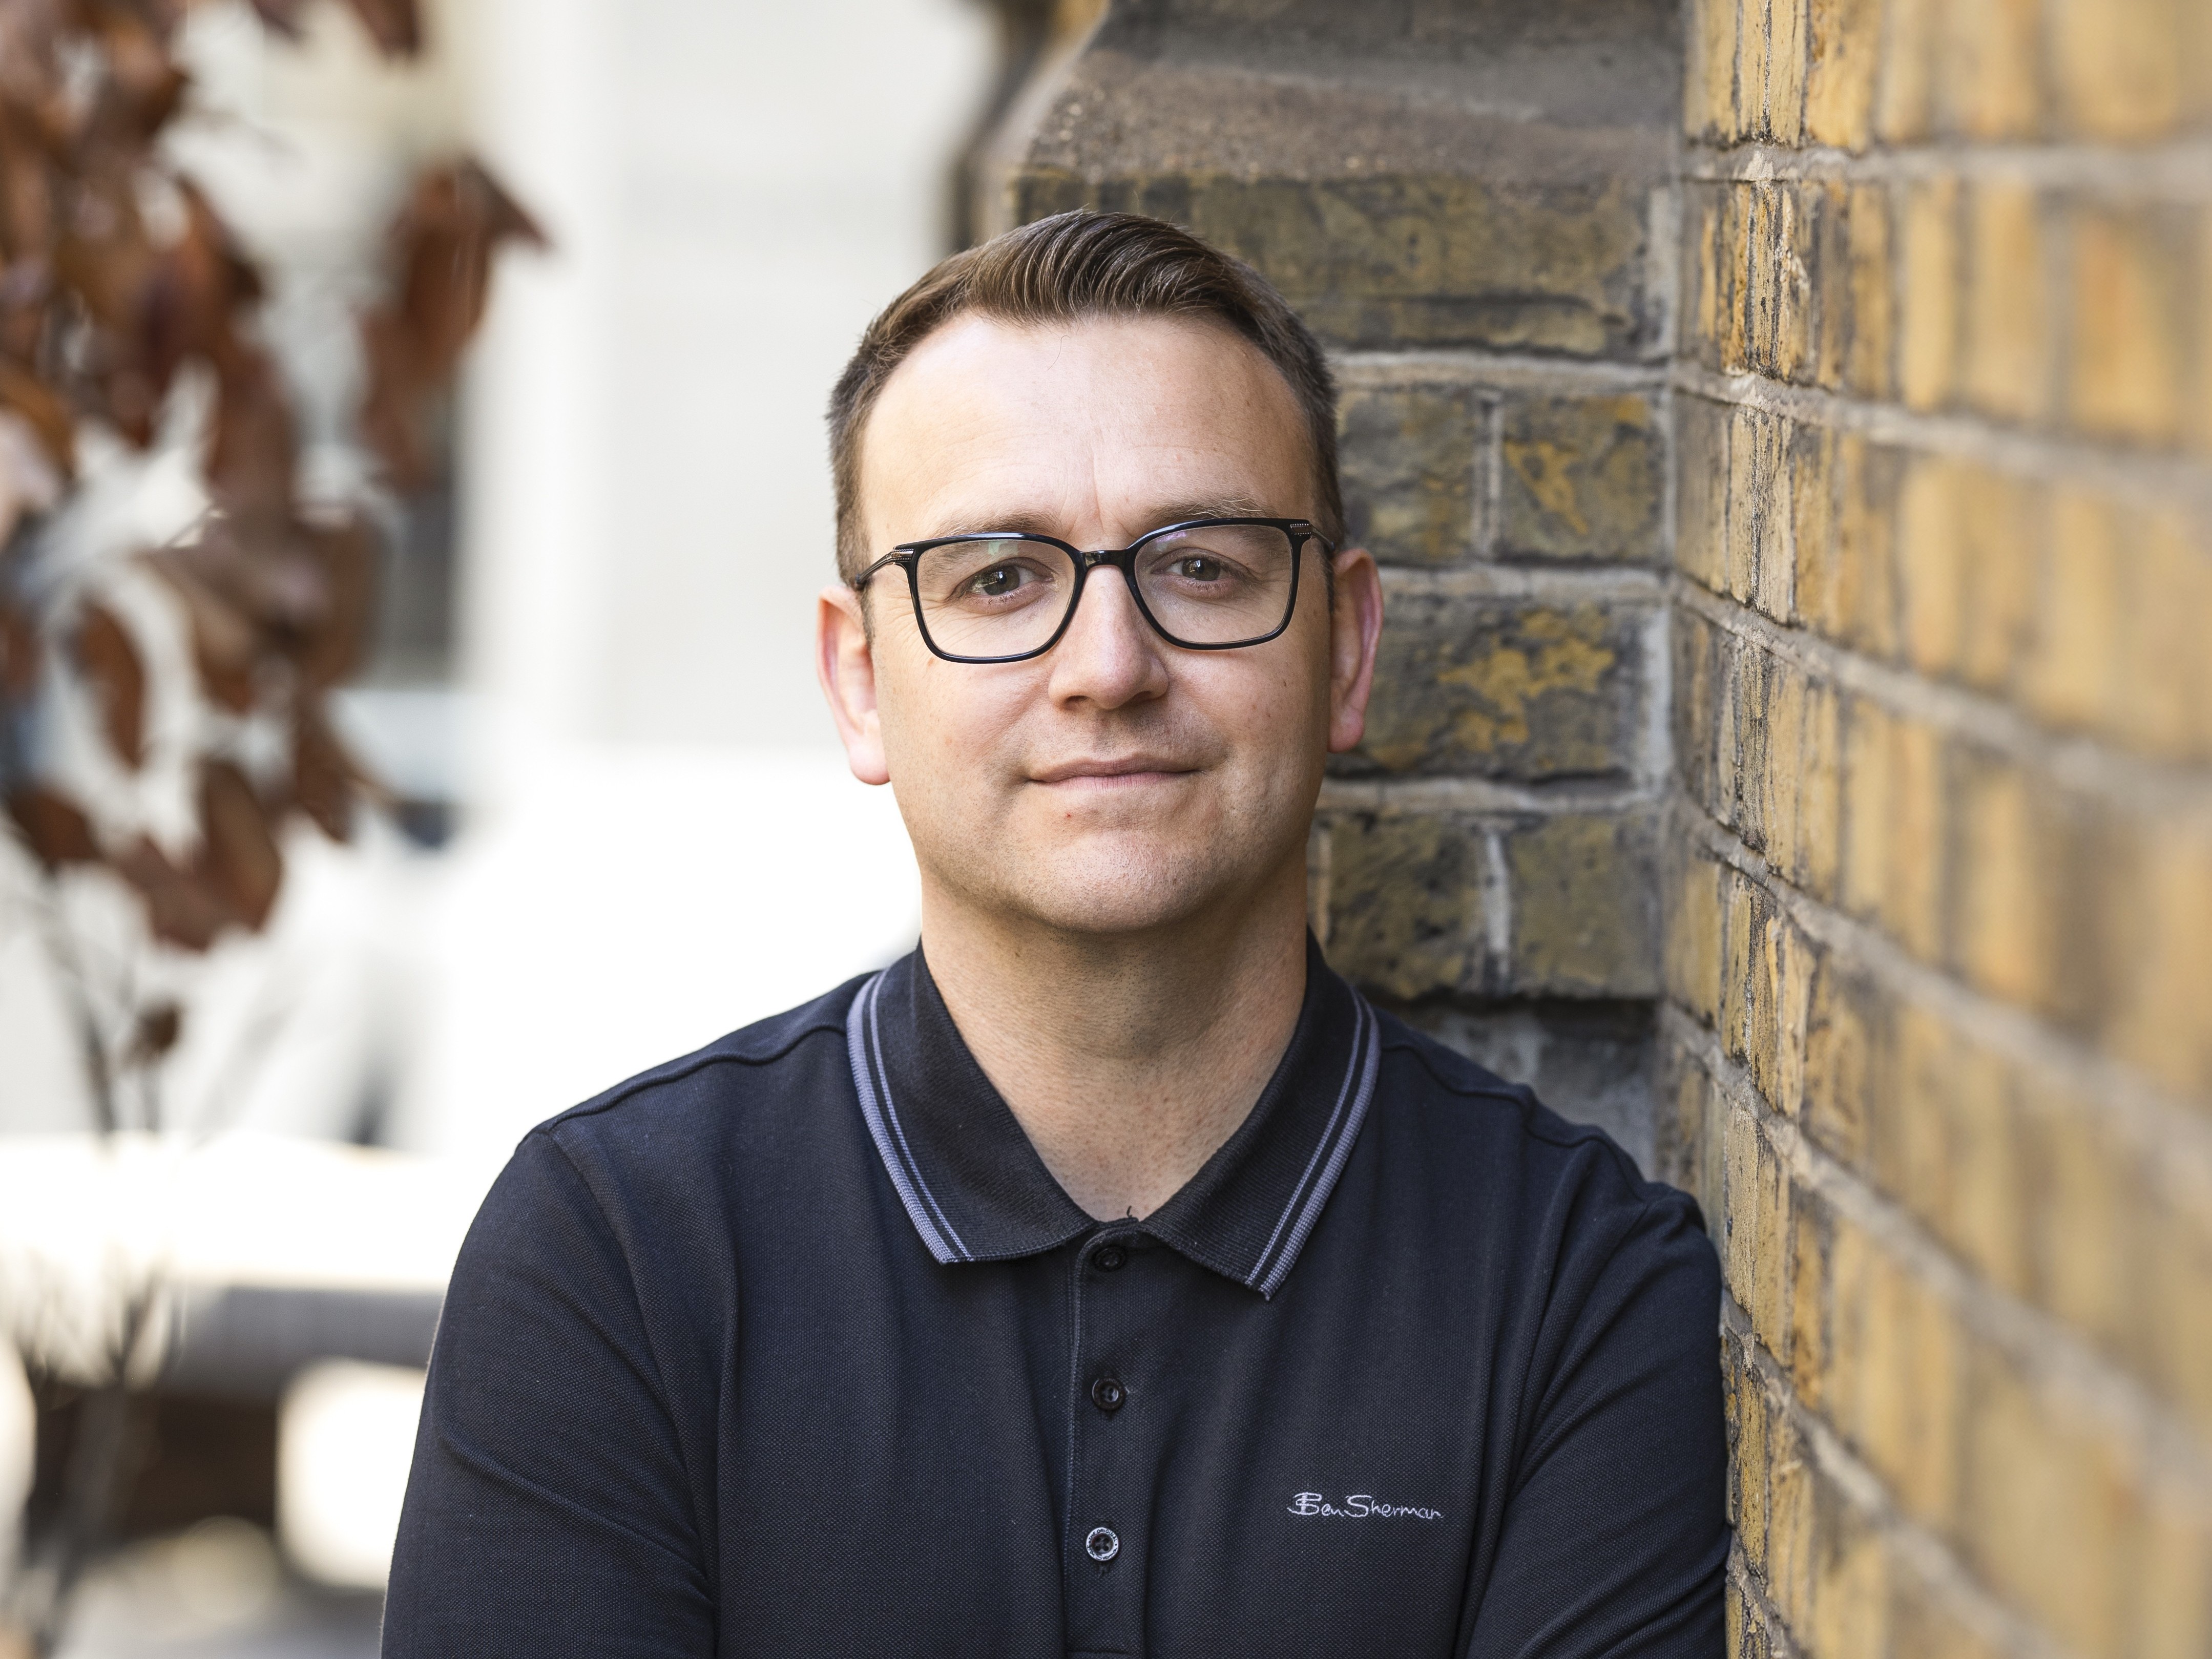
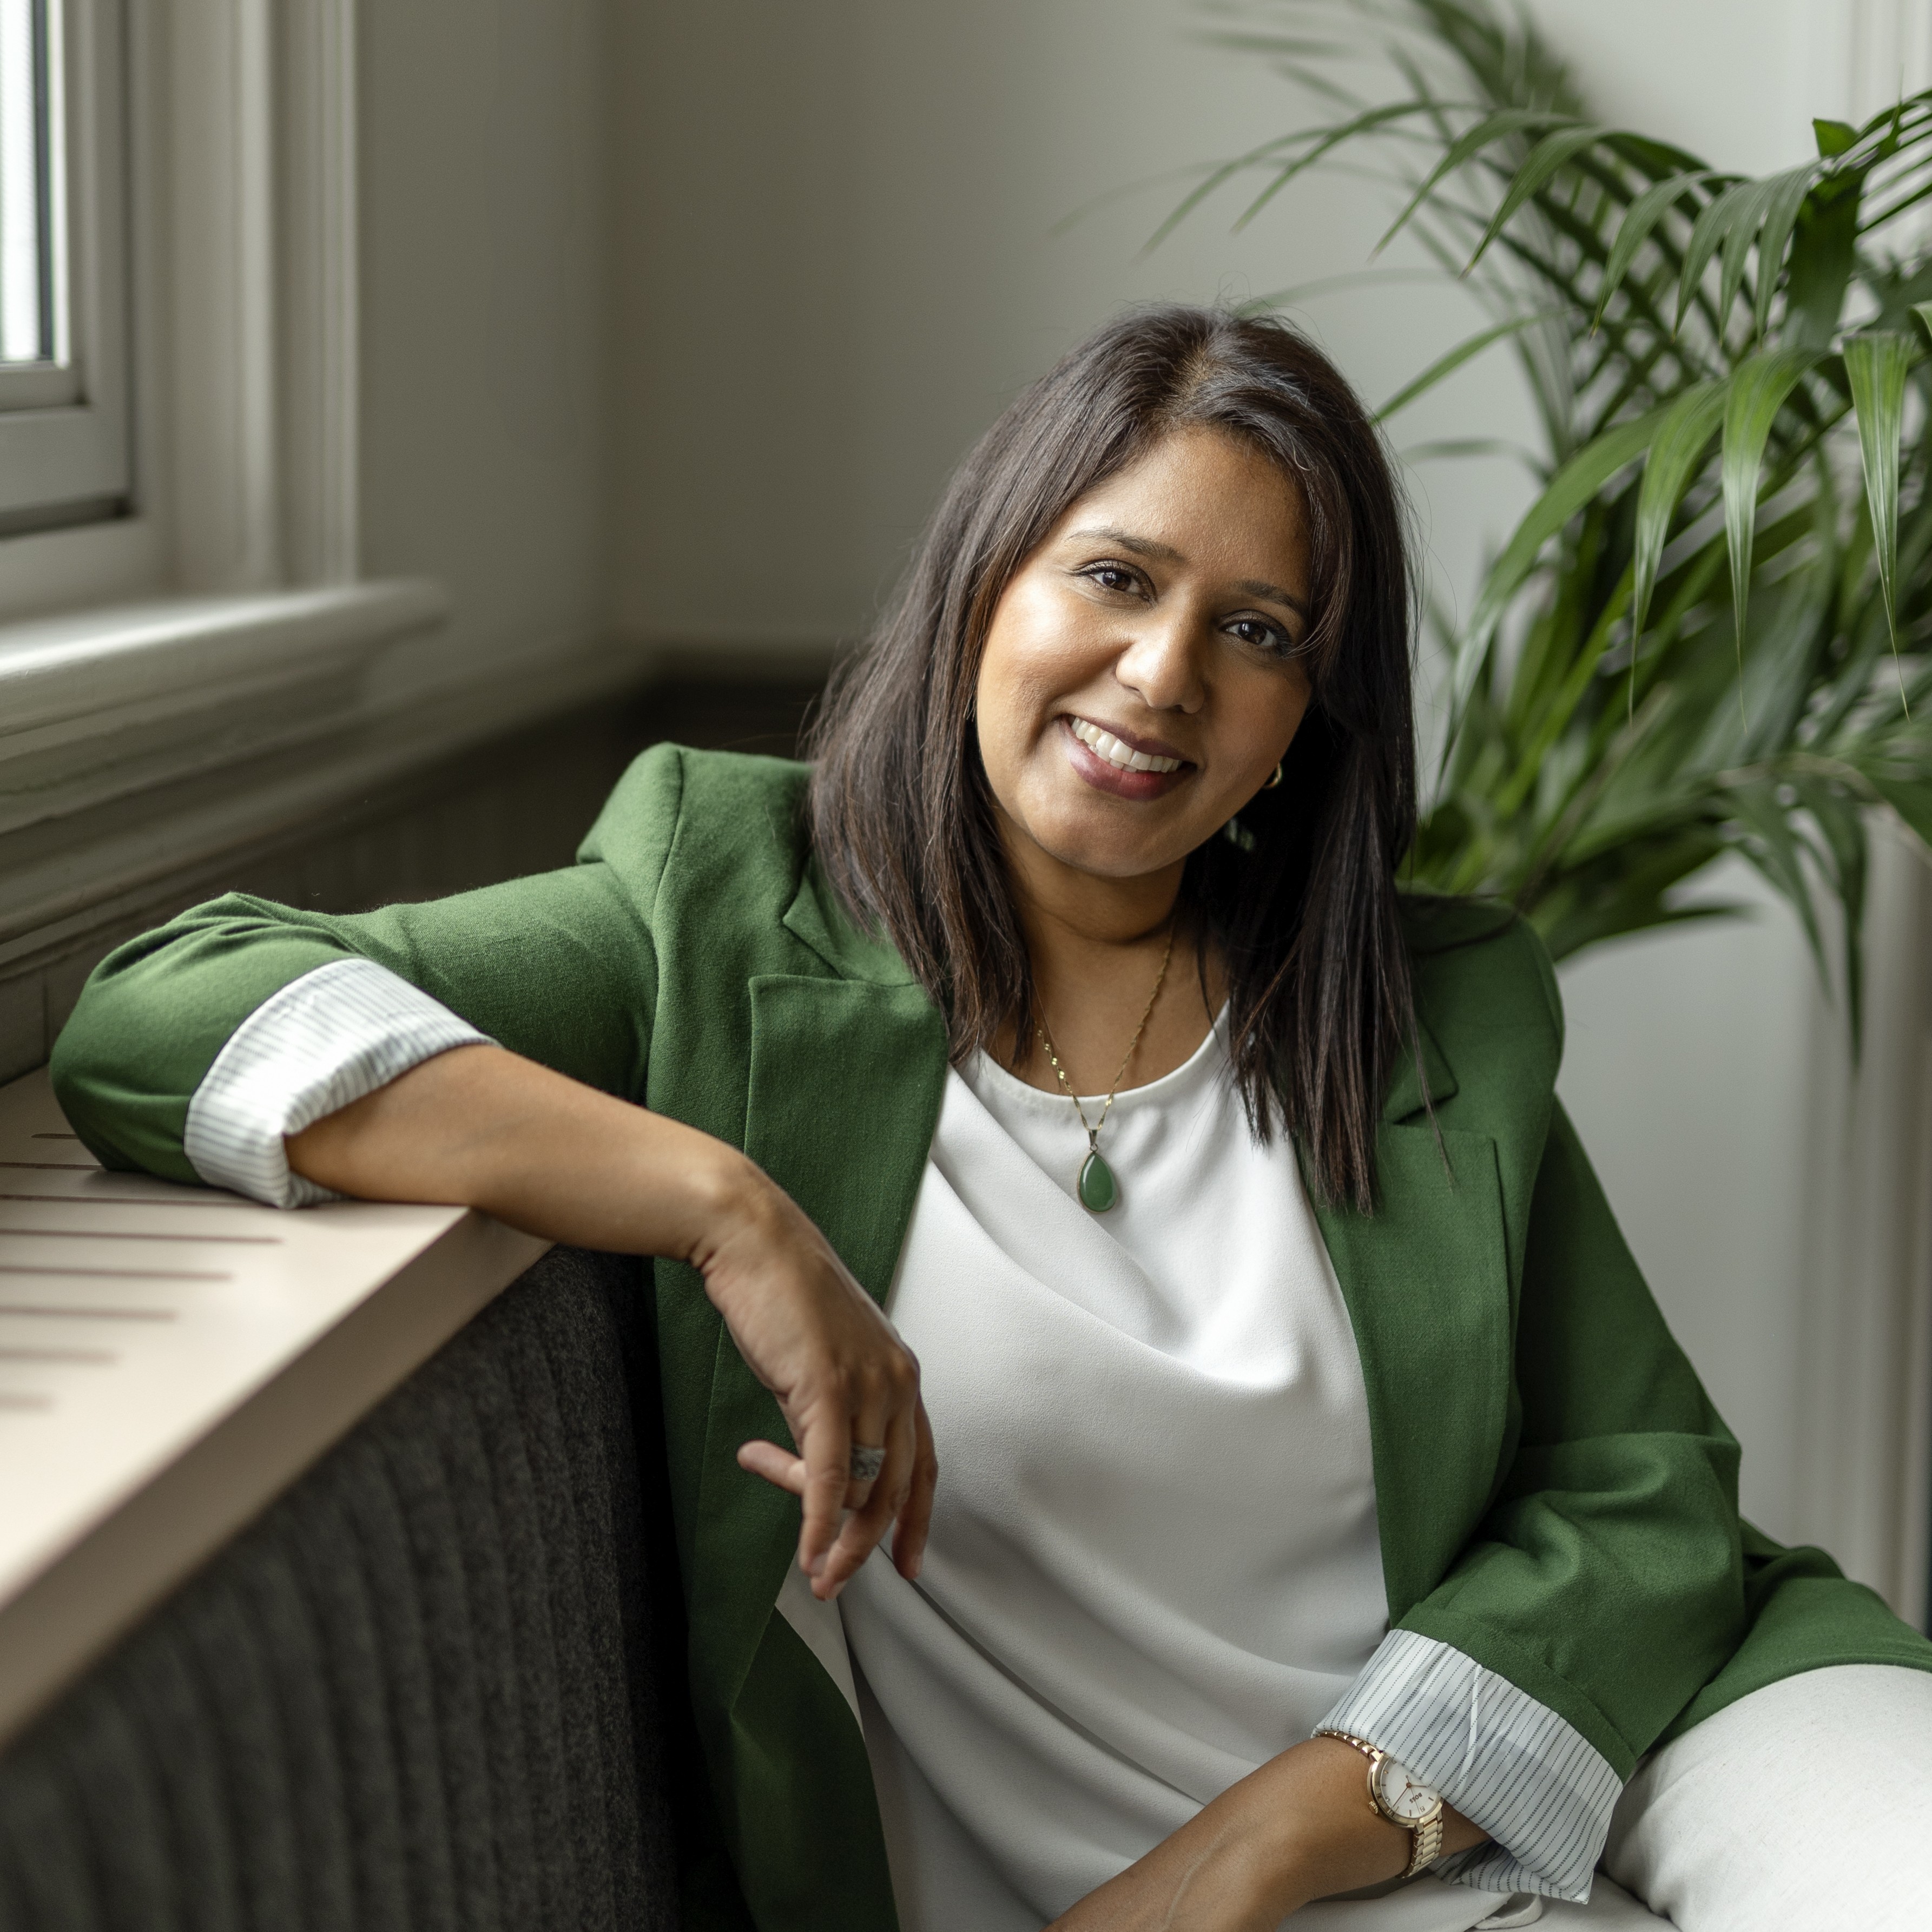
Neelam is a corporate and commercial solicitor with a practical, no-fuss approach to helping businesses get things done.
On the commercial side, she works with agencies, tech companies and growing businesses on the contracts that underpin their operations: drafting, reviewing and negotiating agreements across a wide range of commercial arrangements. On the corporate side, she assists overseas businesses setting up in the UK and forming UK subsidiaries, and has experience of M&A transactions and investment rounds.
Before qualifying as a solicitor, Neelam had a career in legal technology, including as Director of Global Product at LegalZoom. She brings that perspective to everything she does: a deep understanding of what good legal service looks like from the client's side, and how to deliver it.
She's also unfailingly cheerful. Even on Mondays.
When Neelam isn't at her desk, she can often be found upcycling old furniture in her shed, discovering new eateries or testing out recipes on friends and family.
Alistair co-founded Tend Legal with Shona on a simple idea: that small and medium-sized businesses deserve the same quality of legal advice as large companies, without the large firm experience.
As a solicitor with a broad commercial practice, he advises business owners on the full range of issues that come with running and growing a company. That means employment law: advising on settlement agreements, workforce decisions and the day-to-day employment questions that land on founders' desks. It means commercial work: negotiating and reviewing contracts, supplier agreements, and the commercial arrangements that keep a business running. And it means corporate transactions: from business sales and acquisitions to investment rounds, share structures and restructures.
Before co-founding Tend Legal, Alistair was a partner at Woodfords Solicitors in South West London, where he spent over a decade building a reputation for clear, commercial advice to SMEs. He is known for his calm approach, his ability to cut through complexity, and his willingness to give a straight answer.
When not working or acting as taxi driver to his three children, Alistair can be found riding bikes or skateboards, playing various instruments, or at church.
Frequently Asked Questions

It depends on what it says and when it was written. A lot of privacy policies predate the UK GDPR, don't reflect the actual data the business collects, or were copied from another business's website and don't apply to yours. A privacy policy that doesn't reflect what you actually do isn't a defence. It's another problem. We can review what you have and advise on what needs to change.
You need a data processing agreement (DPA) with every supplier that processes personal data on your behalf. That covers most cloud software providers, your payroll provider, email marketing platforms, HR tools, and anyone who hosts your website or customer data. Under UK GDPR, having a compliant DPA in place is not optional: it is a legal requirement. Many businesses are missing these entirely.
You have one month to respond (with a possible extension in limited circumstances). The request must be taken seriously even if it seems unusual or inconvenient. You need to identify all the personal data you hold about the individual, consider any exemptions that might apply, and provide a compliant response. If you've received a Data Subject Access Request (DSAR) and aren't sure what to do, come to us quickly: the clock starts running from the date of the request.
The Act updates several aspects of the UK data landscape, including changes to the legitimate interests basis for processing and to the rules around automated decision-making. The overall UK GDPR framework remains in place, but some of the detail has shifted. We stay current on this and make sure any documents we produce reflect the law as it stands today, not as it stood when the UK GDPR was first introduced.
Increasingly, yes. Data protection has become a standard part of commercial due diligence, particularly for any business that holds significant volumes of personal data (customers, employees, subscribers). Buyers want to see compliant privacy notices, DPAs with key processors, and evidence of a working process for handling data subject rights. Gaps here can affect price or create post-completion risk. Getting your data protection house in order before a sale process starts is worth doing early.